Skip to content

We handle security so your team doesn't

API images are discarded after each call, never used for training without your consent. SOC 2 Type 2 certified, with a live Trust Center for your review.
What you get

Built for the way enterprise teams actually work
SOC 2 Type 2, scoped to our API
Most recent report published April 2026, available in the Trust Center alongside our current controls and policies.

You own what we do with your data

Enterprise contracts default to no model training. Self-serve plans include a customer-controlled opt-out. Either way, images are discarded after each job and training data is stored separately from production data.

Documented and ready for review

Data Processing Agreement, current sub-processor list, encryption posture, and documented incident response process. Available for procurement and legal review.

Workflow

How we handle your data

Sync

Sync API calls

Images sent to sync endpoints are processed in real time and discarded immediately after the response.

Async

Async API jobs

Same models, every surface. Sub-second background removal, AI shadow, resize, format conversion, and brand templates in one workflow.

Log

Defined log lifecycle

Operational logs are deleted after 15 days. API access logs are retained for one year, available to support security investigations and audit requests.

Control

Model training, by contract type

Enterprise contracts don't train by default; self-serve API plans do, with opt-out in settings. On all plans, training and production data stay separate, and training-data access is limited to the ML team.

Data protection

Encrypted at every stage, on trusted infrastructure
  • All traffic is encrypted with TLS 1.2 or higher, managed through Cloudflare.

  • Data at rest is encrypted at the infrastructure layer by our cloud hosting providers. (GCP and AWS)

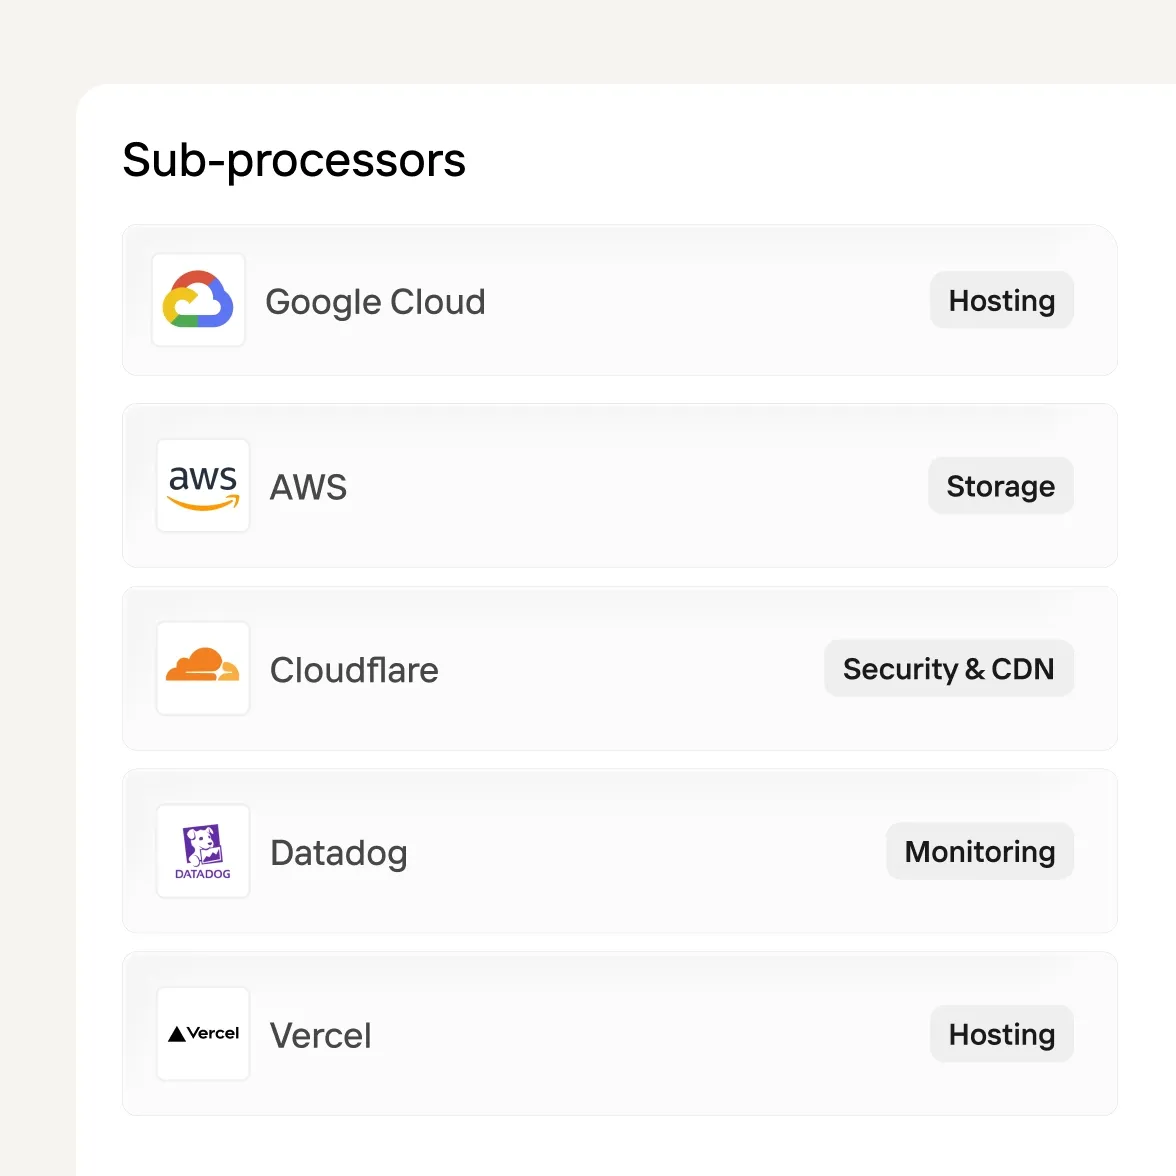
  • The current sub-processor list is published for API customers and refreshed the list evolves. GCP and AWS hosting and storage, Cloudfare for CDN, security, and DNS, Datadog for event logging and API parameter logs, and Vercel for hosting.

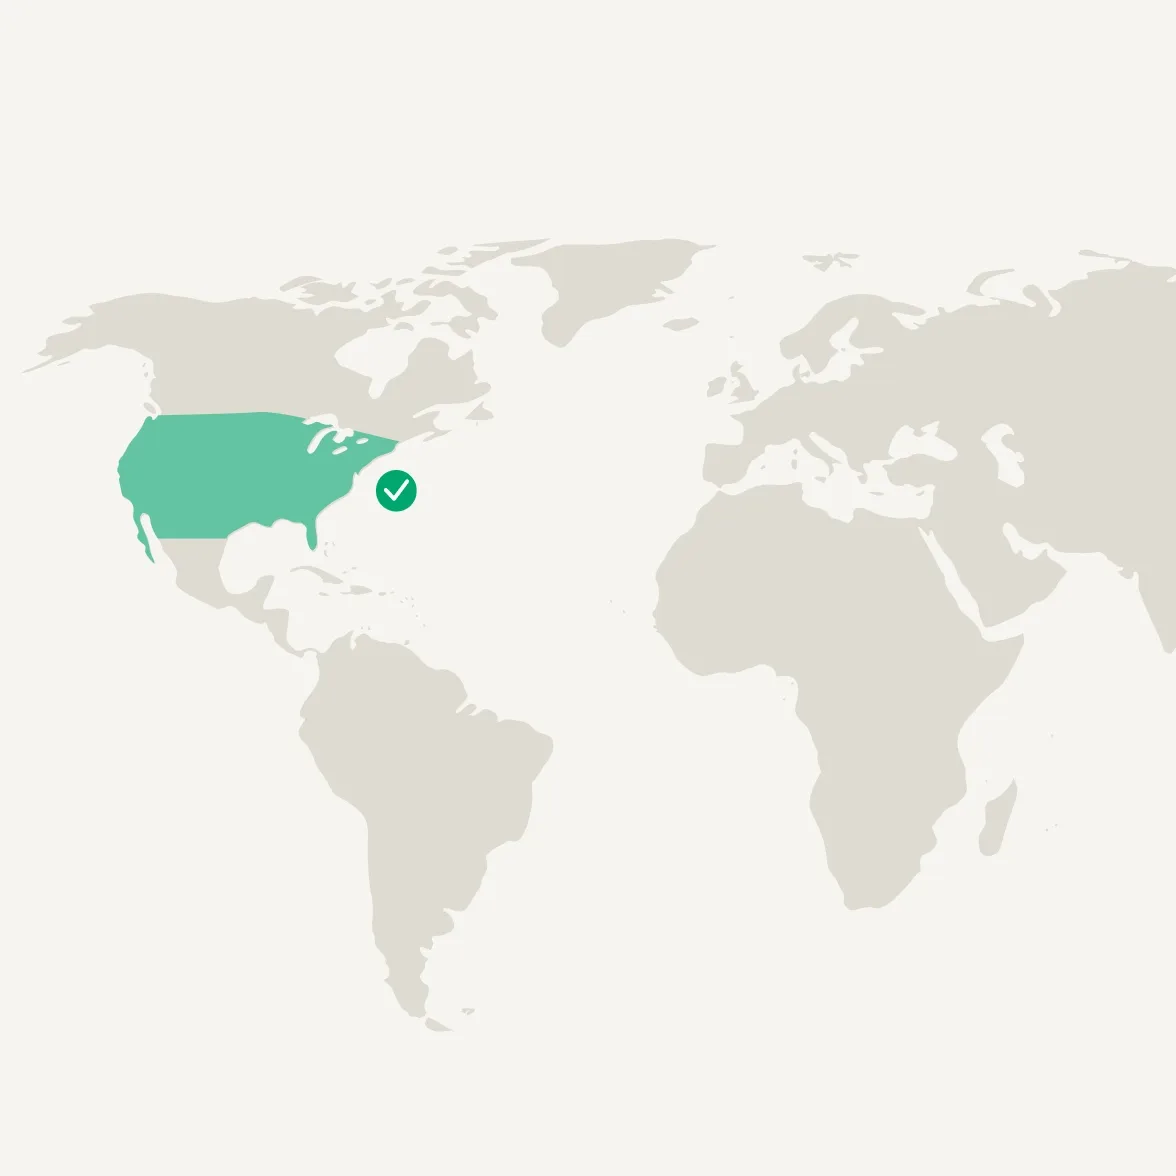
  • Our infrastructure runs in the United States. EU-only data residency isn't available today. If regional residency is a contract requirement, raise it with sales early so we can scope what's possible.

Encryption
Governance and incident response

Documented incident response, clean track record

Data Processing Agreement

Data Processing Agreement

A documented process covering immediate containment, GDPR breach notification, and post-incident analysis.

Track record

Track record

One incident on record (October 2024): a 30-minute service availability disruption. No customer data was compromised. Documented and reviewed against our incident response process.

Transparent breach reporting

Transparent breach reporting

If there is a data breach affecting your personal data, we have a GDPR compliant reporting process, and we strictly follow our information obligations.

Trust & Security

Trusted by businesses worldwide

Photoroom meets SOC 2 Type 2 standards for its API and is fully GDPR-compliant, ensuring strong security, availability, and data privacy.
Frequently asked questions

Is Photoroom SOC 2 certified, and what's in scope?

Yes. Photoroom holds a SOC 2 Type 2 attestation scoped to our API service. The most recent report (April 2026) and current controls are available in the Trust Center. If your procurement requires evidence on a different scope, raise it with the sales team early.

Is Photoroom GDPR-compliant? And is a DPA available?

Yes to both. We operate under GDPR principles, with a documented sub-processor list, a defined breach notification process, and personal data anonymization before any model training. A Data Processing Agreement is available for Enterprise customers through your account team.

Are customer API images used to train Photoroom’s models?

It depends on your contract.

  • Enterprise contracts: no by default. Training only happens if explicitly agreed in writing.

  • Self-serve API plans: no. Images sent through the API aren't used to train AI models.

  • All plans: training data and production data are stored separately. Training-data access is restricted to ML team members, with every access logged.

Where is data hosted, and how is it encrypted?

Our infrastructure runs on Google Cloud Platform and Amazon Web Services in the United States. Data in transit is encrypted with TLS 1.2 or higher (managed through Cloudflare). Data at rest is encrypted at the infrastructure layer by GCP and AWS. EU-only data residency isn't available today. If regional residency is a contract requirement, raise it with sales early.

How long is data retained?

Sync API images are discarded as soon as the response returns. Async API images are retained briefly while the job runs, then discarded. Operational logs are deleted after 15 days. API access logs are retained for one year, available to support security investigations and audit requests.

Who are Photoroom's sub-processors?

GCP and AWS for hosting and storage, Cloudflare for CDN, security, and DNS, Datadog for event logging and API parameter logs, and Vercel for hosting. The current list is published in the Trust Center.

Had Photoroom ever had a security incident?

One incident on record (October 2024): a 30-minute service availability disruption. No customer data was compromised. The event was documented and reviewed against our incident response process.

Do app users have a training opt-out?

Yes. App users can opt out of contributing to model improvement through a toggle in account settings. When data is used for training, personal data is anonymized first. Note: this is separate from the API customer commitment, where images aren't used to train AI models on self-serve and Enterprise API plans alike.

Start selling at first sight

Get listing-ready product visuals in seconds.